 Proofroom
Audit evidence that collects itself.
Proofroom keeps you ready for PCI DSS and SOC 2 all year: it pulls evidence from the systems you already use, routes it for review, and has it waiting when the auditor asks.
What it replaces
Screenshots chased by email
Connectors collect evidence on schedule from the systems you use, with guided exports for the rest: 47 systems in all.
A spreadsheet of controls
Every control, its owner, the evidence it needs and when, mapped across PCI DSS and SOC 2.
The scramble before the audit
Readiness is tracked every day, so gaps show up months ahead, not the week before.
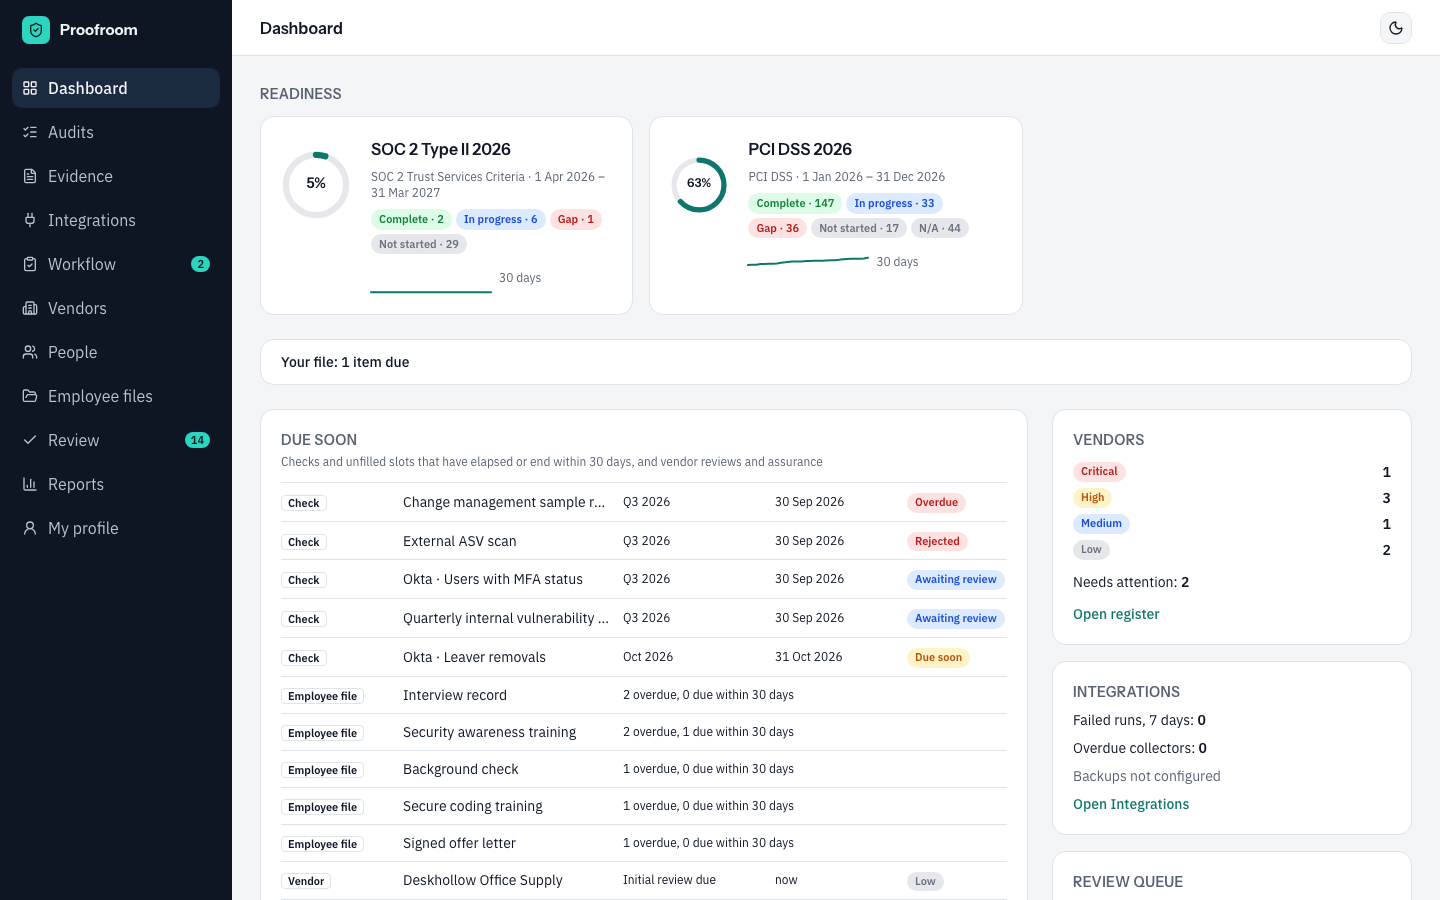
Readiness you can see
Each audit shows how ready you are, control by control, with a 30-day trend.
Gaps and anything due soon are listed first, so nothing waits for the week before the audit.
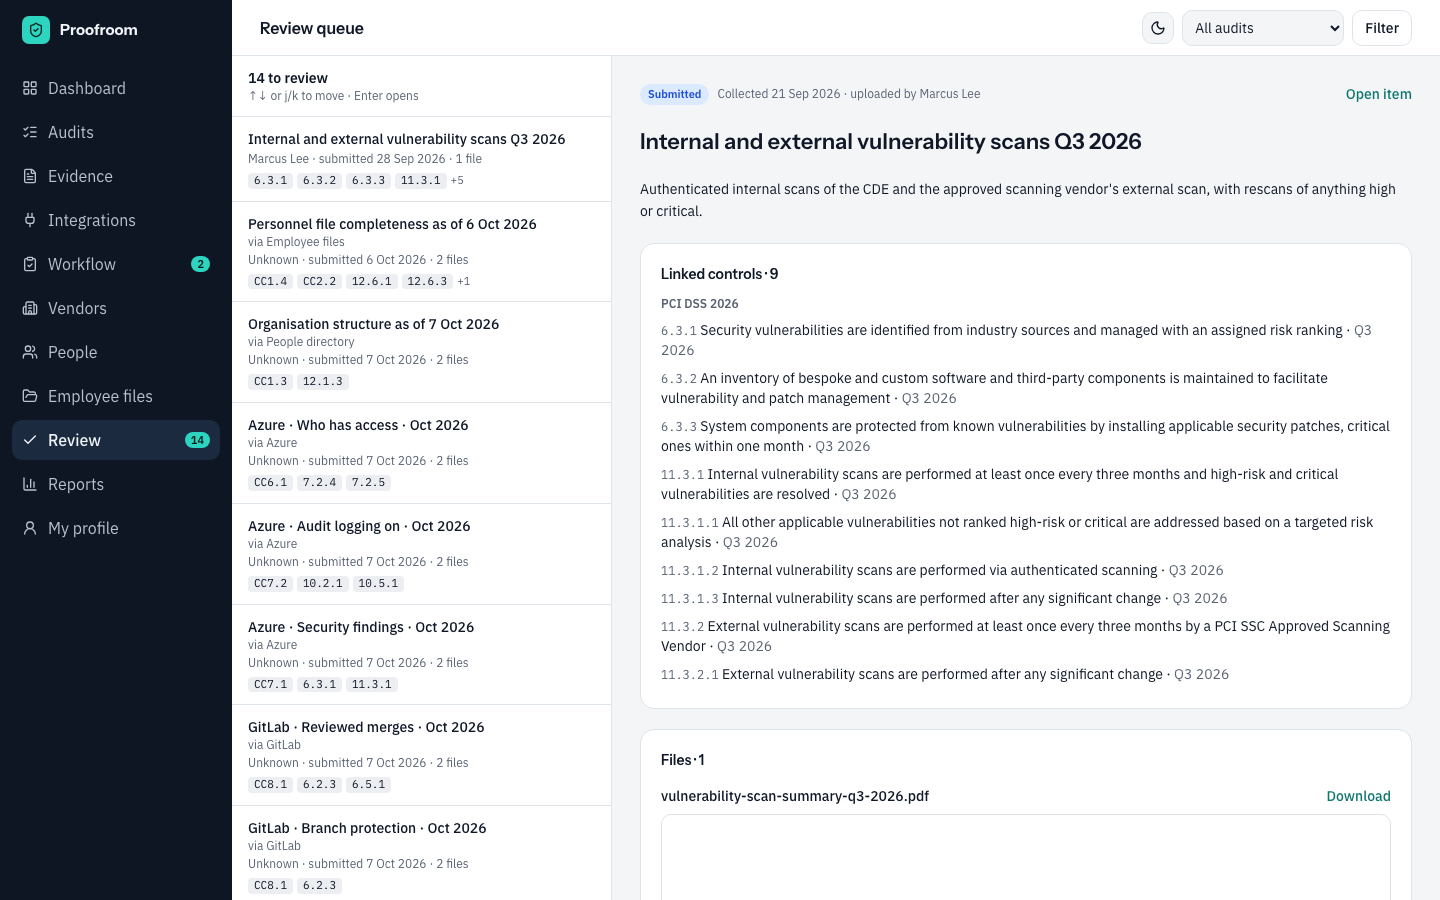
Evidence, reviewed
Analysts submit evidence; a reviewer accepts it or rejects it with a reason. Every version is kept.
Auditors see exactly what was accepted, by whom and when.
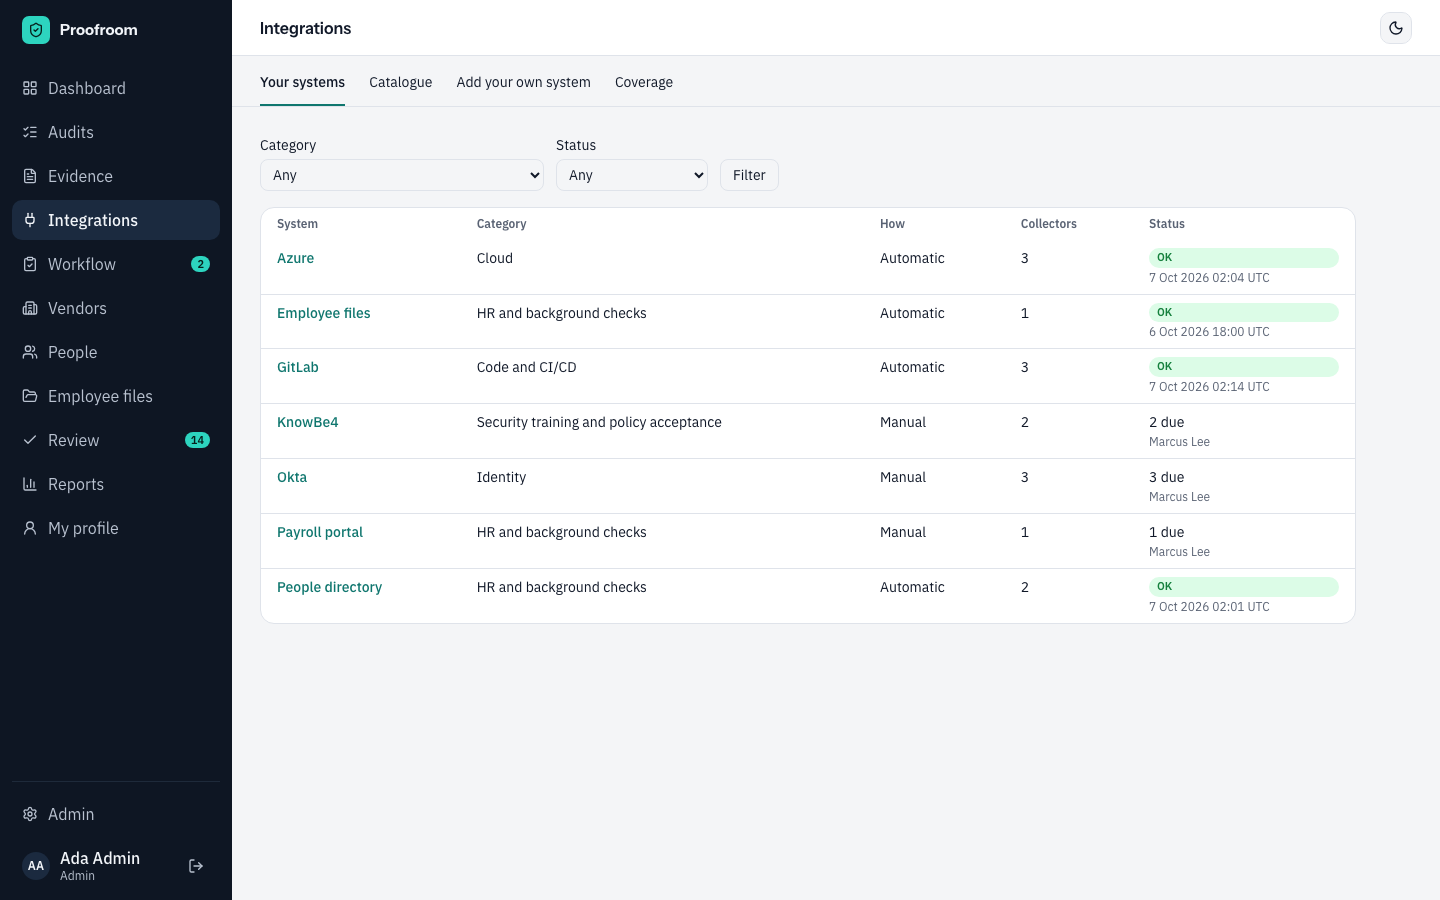
Connectors that do the collecting
Connect your identity provider, cloud, code host, ticketing and on-call tools once.
Access reviews, change approvals and incident records arrive on schedule, linked to the right controls.
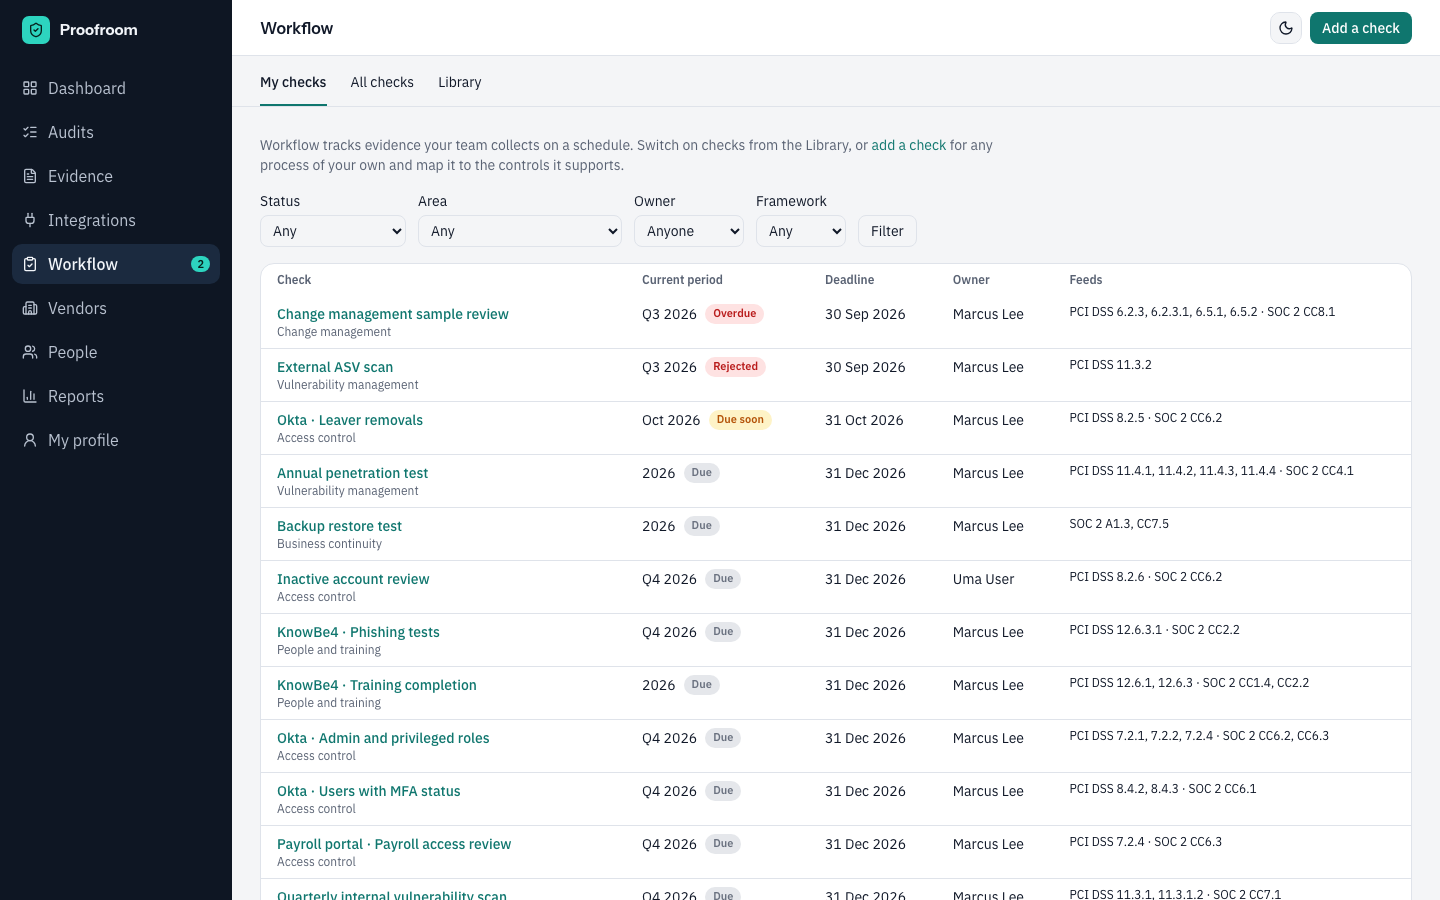
Recurring work, assigned
Quarterly reviews and one-off tasks have an owner, a reviewer and a due date.
A major incident opens its own post-incident review task.
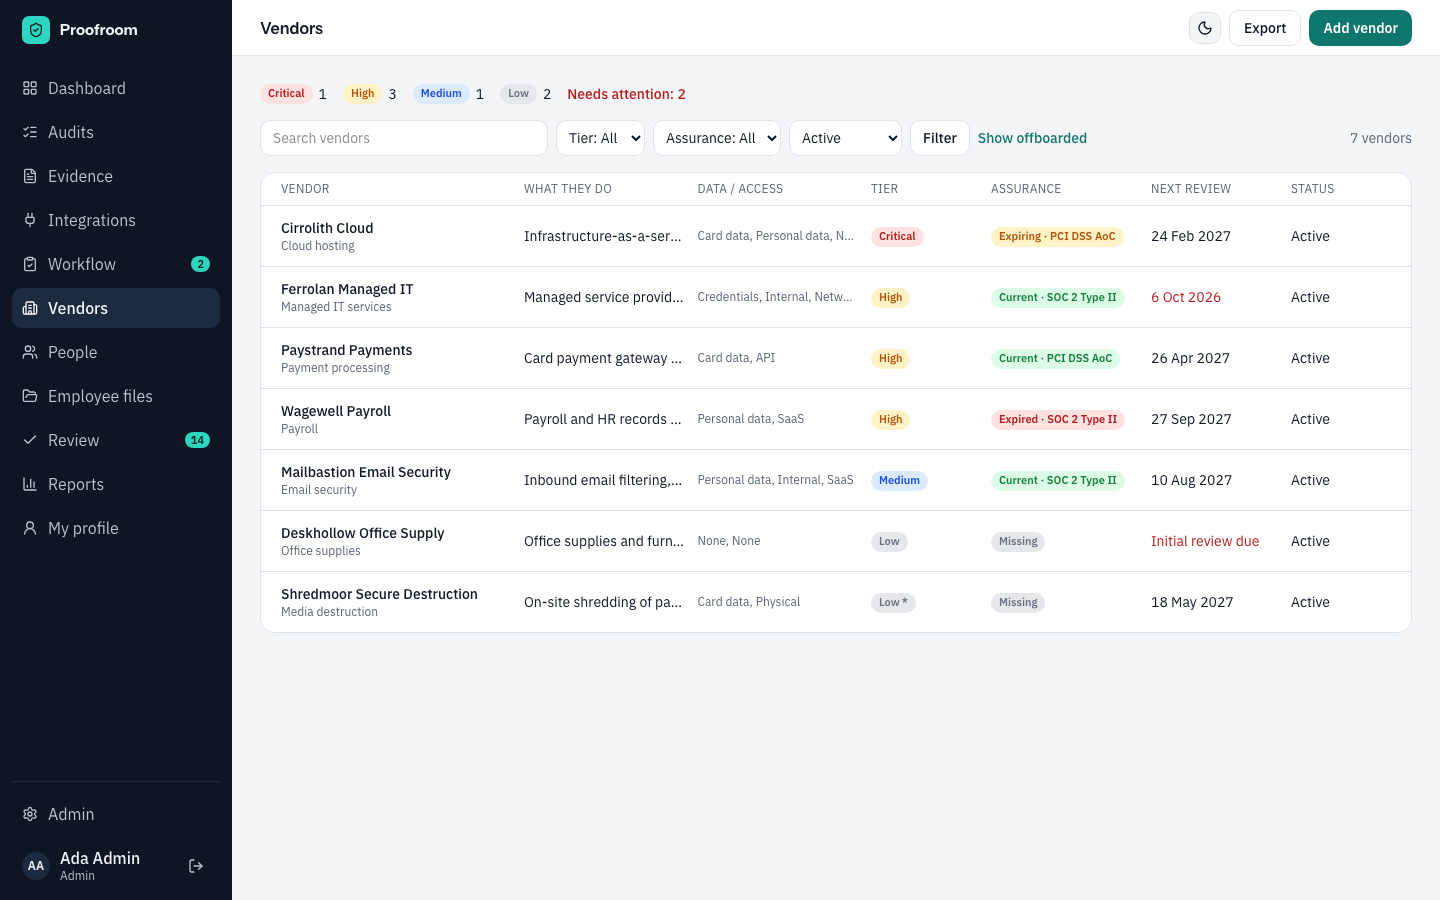
Vendors in one place
Rank vendors by risk, track their SOC 2 reports and attestations, and see what expires next.
Responsibility for each requirement is recorded per vendor.
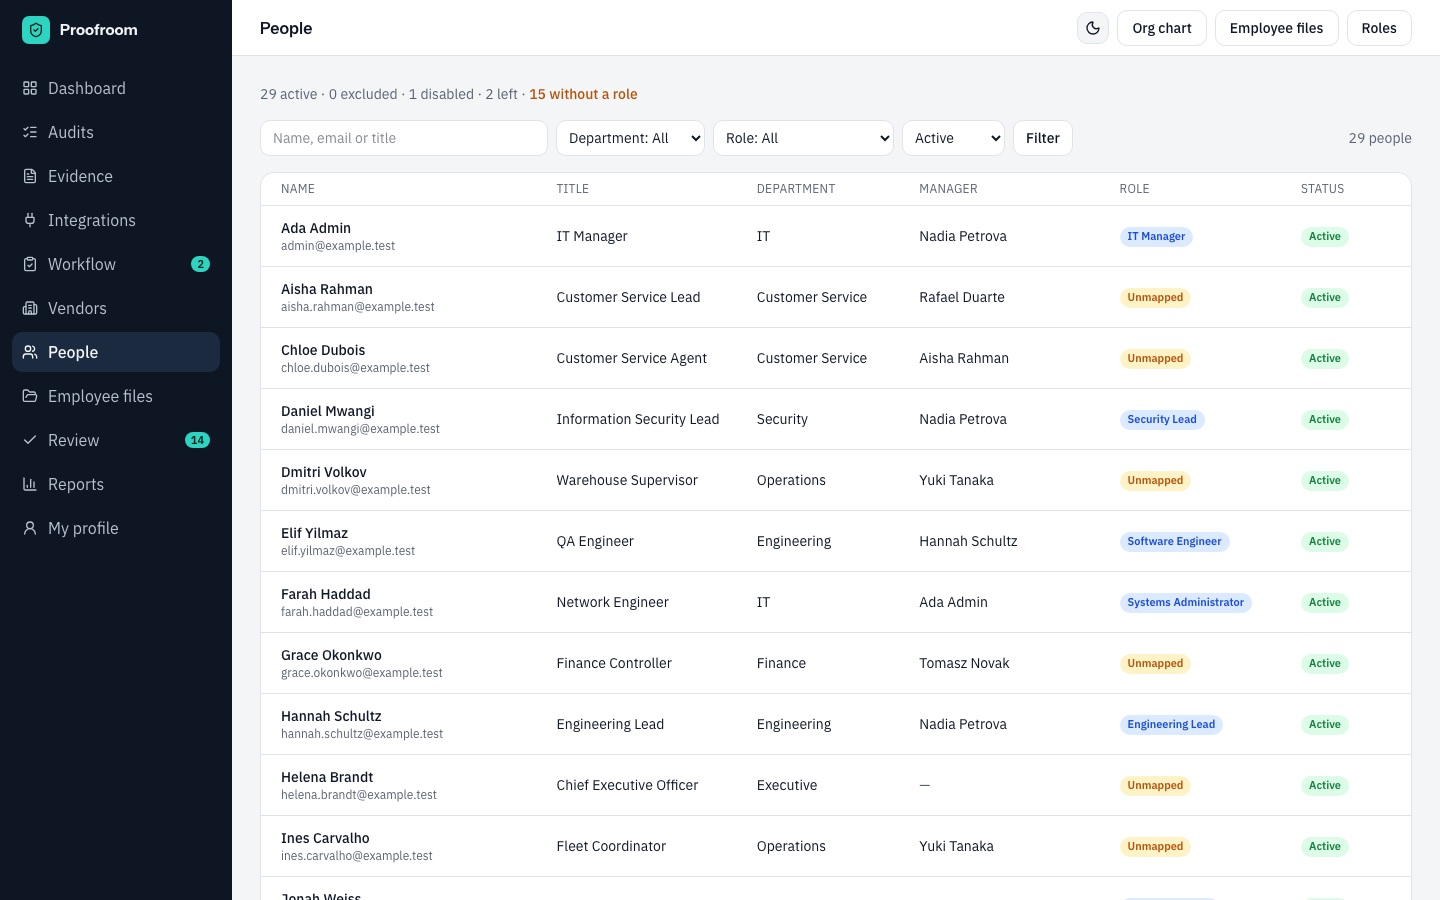
People and roles
Your directory keeps the people list current: joiners, movers and leavers.
Roles own controls, so the right person is asked for the right evidence.
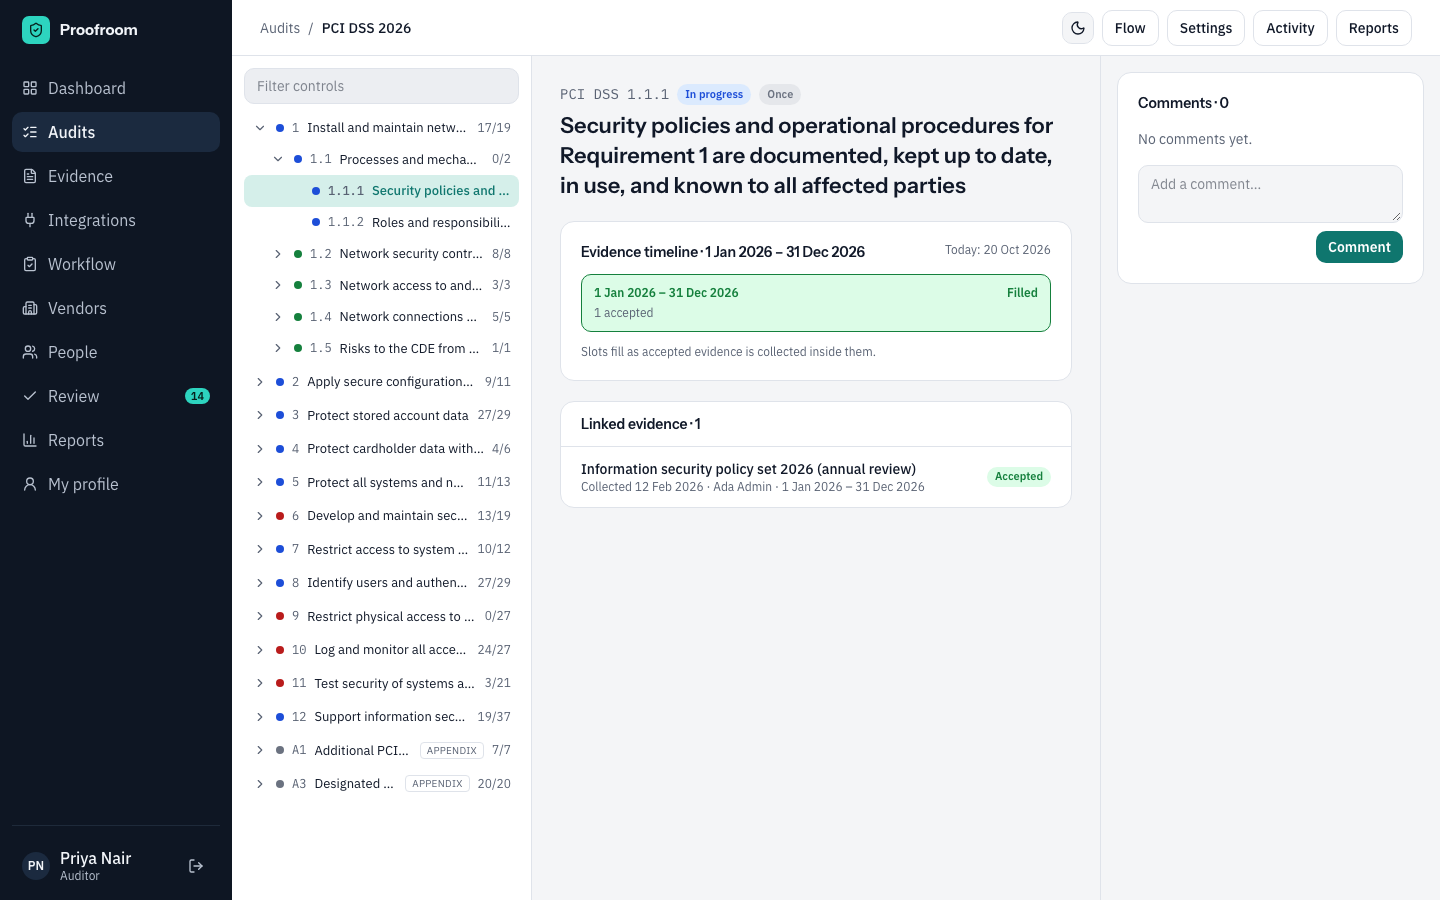
Room for your auditor
Invite your auditor to read the evidence, comment on controls and follow the activity log.
They change nothing; you keep one copy of the truth.
See it with real-looking data in one click.
A made-up freight company, a year of evidence, and every role to try. No sign-up.